Elena Simon · 18 October 2026
Regulatory Navigation in Global Academic Computing Collaborations
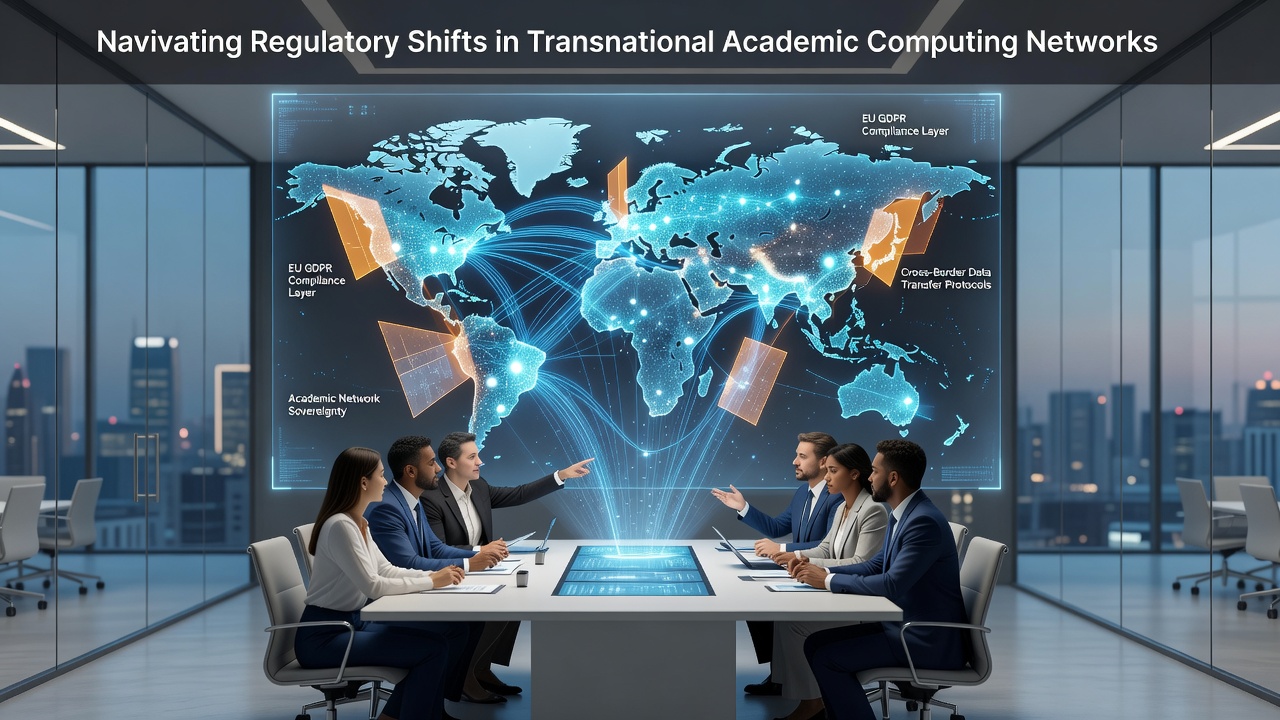
Academic institutions around the world now face mounting pressure to align their computing infrastructures with shifting international regulations that govern data flows, security standards, and cross-border research partnerships, and these changes affect everything from shared cloud resources to high-performance computing clusters used in joint scientific projects.
Current Regulatory Frameworks Shaping Academic Networks
Multiple jurisdictions have updated their rules on data sovereignty and privacy protections in recent years, with the European Union's data protection mechanisms continuing to influence how research consortia handle personal and sensitive datasets across member states and partner countries, while similar updates in North America and Asia Pacific regions have introduced new requirements for encryption and audit trails. Researchers who manage transnational networks must track these developments closely because non-compliance can halt data exchanges and delay collaborative experiments that rely on real-time processing across continents.
Data from international oversight bodies shows that academic computing projects involving multiple countries increased by over 40 percent between 2022 and 2025, which has prompted regulators to focus on interoperability standards that allow secure information sharing without violating local laws. Observers note that frameworks such as those outlined by the OECD on digital security have become reference points for universities seeking to harmonize their policies across borders.
Key Challenges in Compliance and Data Mobility
One persistent difficulty arises when institutions must reconcile differing definitions of sensitive data, since what counts as personal information under one national statute may fall outside protections elsewhere, forcing network administrators to implement layered access controls and consent management systems that satisfy all participating parties. This situation becomes especially complex during large-scale initiatives like climate modeling or genomic research that aggregate datasets from dozens of sources simultaneously.
Another issue centers on the speed of regulatory updates, because new directives often take effect with limited advance notice, leaving academic teams scrambling to audit existing workflows and renegotiate service agreements with cloud providers. In October 2026 several updated provisions on cross-jurisdictional data transfers are scheduled to activate in multiple regions, which will require institutions to demonstrate enhanced accountability measures including regular third-party assessments and documented risk evaluations.
Technical teams frequently discover that legacy systems lack the granular logging capabilities demanded by newer standards, prompting investments in upgraded monitoring platforms that can generate compliance reports on demand. Those who've studied these transitions report that early adoption of modular architectures helps organizations adapt without disrupting ongoing research activities.
Strategies Employed by Research Institutions
Many universities have established dedicated compliance offices that coordinate with legal experts and IT specialists to map regulatory requirements against operational needs, and these groups often develop internal playbooks that outline step-by-step responses to common scenarios such as data subject access requests or breach notifications. Partnerships with national research agencies have also proven useful, since these bodies sometimes provide guidance documents and training sessions tailored to academic environments.
Evidence suggests that adopting federated identity management tools allows researchers to maintain secure access across networks while meeting authentication standards set by various governments. Institutions that have implemented such systems report smoother collaboration with international colleagues because the technology reduces friction associated with repeated credential verifications.
What's interesting is how some consortia now embed regulatory review stages directly into project planning cycles, ensuring that compliance considerations shape network design from the outset rather than appearing as afterthoughts. This approach has helped avoid costly retrofits when new rules emerge.
Looking Ahead to Future Developments
Anticipated advancements in regulatory technology, including automated compliance checking tools powered by machine learning, may soon assist administrators in monitoring policy changes across multiple jurisdictions in real time. Government agencies in several countries have begun piloting such platforms for public sector research networks, and academic groups are watching these trials to assess scalability for their own use cases.
Continued dialogue between regulators and the higher education sector remains essential because feedback from practitioners can inform more practical rule-making that supports scientific progress while safeguarding data integrity. Organizations such as the National Institute of Standards and Technology have published resources on secure computing practices that serve as benchmarks for institutions worldwide.
Conclusion
Transnational academic computing networks continue to evolve under the influence of dynamic regulatory environments, and success depends on proactive monitoring, flexible technical infrastructure, and sustained coordination among stakeholders. Institutions that integrate compliance into core operations position themselves to maintain productive international partnerships even as rules shift in the years ahead.